
Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance
Taiwan absorbs more than 2.4 million foreign cyberattacks a day, and the actors behind them point, without exception, to APT groups backed by the Chinese state (officially described as "PRC-linked," or in Taiwan's own terminology "CCP cyber forces" — whether they belong to a specific People's Liberation Army unit remains unconfirmed). Government agencies, critical infrastructure, and supply chains are all on the target list. Three years after the Ministry of Digital Affairs was founded, a zero-trust architecture is being rolled out — but one unpatched computer in a county or city government office could cost an entire city its power.
Article contents01 / 06
- National Security Bureau data: government networks logged an average of 2.4 million intrusion attempts a day in 2024; after the 2025 statistics expanded the scope to 9 categories of critical infrastructure including government agencies, the daily average reached 2.63 million (up 6% from the 2.46 million figure for 2024 restated under the same expanded scope). There were 906 major cybersecurity incidents for the full year, with more than 80% targeting government agencies, and the actors behind them are multiple APT groups backed by the Chinese state (whether they belong to a specific People's Liberation Army unit remains unconfirmed).
- Taiwan's main threats: BlackTech has long lurked inside government and telecom networks (since at least the 2010s; its targeting of Taiwan rests on industry threat intelligence, while the official joint advisory confirms only the U.S. and Japan), Flax Typhoon has implanted itself in infrastructure (disclosed by Microsoft in 2023), and Volt Typhoon has pre-positioned lateral-movement capability — its link to a Taiwan Strait conflict is an intelligence assessment, not an official confirmation; all three have clear nation-state attribution.
- The Ministry of Digital Affairs was founded in August 2022, and a zero-trust architecture is being rolled out in three phases (2023-2026); but the share of IT budgets Taiwanese SMEs devote to cybersecurity is widely believed within the industry to be markedly low (observation, low confidence; not an official statistic), and the government supply chain is the weakest link — a backdoor through a single software contractor beats a frontal assault on a fully defended government data center.
“Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance” reports that 2024 Major Cybersecurity Incidents(906 incidents)。 More than 80% (about 726 incidents) targeted government agencies and public services [1]。
“Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance” reports that Trend in Daily Foreign Cyberattacks (10,000s per day)(Daily Attack Count)。 2023: 1.2 million/day under the government-network definition, or 1.23 million/day under the critical-infrastructure definition; 2024: 2.4 million/day under the government-network definition; from 2025 the definition shifted to 9 categories of critical infrastructure, reaching 2.63 million/day (restated as 2.46 million/day for 2024 under the same definition) [1][2]。
“Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance” reports that Timeline of Major APT Incidents(BlackTech Has Lurked for Over 7 Years)。 BlackTech (2010s–), Flax Typhoon (2021–), Volt Typhoon (2019–); Flax Typhoon's targeting of Taiwan is confirmed by an official document, while BlackTech's and Volt Typhoon's targeting of Taiwan rest on industry threat intelligence and intelligence assessments (observation; medium confidence) [3][4][10]。
Three A.M., a Document in the Inbox
At three in the morning on a Monday in the fall of 2024, an email sat quietly in the inbox of a civil servant in a county or city government in central Taiwan, attached with what appeared to be an official document from the Executive Yuan. The subject line read "Urgent: Notice of 2025 Budget Approval," and the attachment was a Word file.
This was not a normal official email. The Executive Yuan never sends documents in the middle of the night, and it certainly would not wrap a budget notice inside an attachment. But the civil servant who received it did not know that. He opened the attachment. Within milliseconds, a piece of malicious code quietly executed on his computer and began connecting to a server abroad.
This is a textbook case of spear-phishing, and it is one of more than 906 major cybersecurity incidents that hit Taiwan in 2024 [1]. Not every case begins this clearly, but almost every one points in the same direction: sitting on the other end is an APT (advanced persistent threat) group backed by the Chinese state — official documents mostly call it "PRC-linked" or, in Taiwan's own terminology, part of the "CCP cyber force," and whether it belongs to a specific People's Liberation Army unit is not confirmed by any source this article could trace (inference; medium confidence).
“Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance” reports that 2024 Major Cybersecurity Incidents(906 incidents)。 More than 80% (about 726 incidents) targeted government agencies and public services [1]。
Taiwan's cyber front line is a door struck by 2.4 million attacks every day. On the other side of that door sits a Ministry of Digital Affairs founded only three years ago, tens of thousands of government units with wildly uneven cybersecurity capability, and countless small and medium-sized businesses that take on government work without ever having undergone a formal cybersecurity audit. This article is not about whether that door is being guarded well or badly — it is about where the mechanism guarding it came from, what holes remain, and who should be responsible for patching them.
1. 2.4 Million a Day: What Is Behind the Number?
What does 2.4 million cyberattacks a day actually mean? Do the math: that works out to roughly 27.8 attacks per second, about 1,667 per minute. If every attack is imagined as one attempt to break down a door, Taiwan's digital border is a door being pounded on more than 1,600 times a minute.
This figure comes from the National Security Bureau's annual cybersecurity threat report, published in 2025 [1]. The average daily attack count under the government-network definition was 2.4 million in 2024; after the 2025 statistics expanded the scope to 9 categories of critical infrastructure including government agencies, the daily average reached 2.63 million [2] (restated as 2.46 million for 2024 under that same expanded definition, roughly a 6% year-on-year increase). This does reflect a real increase in attack volume, but it also reflects an expanded measurement scope — the two figures should not be read as points on a single continuous trend line.
“Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance” reports that Trend in Daily Foreign Cyberattacks (10,000s per day)(Daily Attack Count)。 2023: 1.2 million/day under the government-network definition, or 1.23 million/day under the critical-infrastructure definition; 2024: 2.4 million/day under the government-network definition; from 2025 the definition shifted to 9 categories of critical infrastructure, reaching 2.63 million/day (restated as 2.46 million/day for 2024 under the same definition) [1][2]。
These attacks have a clear order of priority in their targets. According to the National Security Bureau's "Analysis of Chinese Communist Cyberattack Patterns Against Taiwan, 2024," government agencies accounted for more than 80% of the 906 major cybersecurity incidents [1]. Attacking the government serves two strategic purposes: first, stealing intelligence (personnel data, policy documents, defense procurement information); second, pre-positioning backdoors for rapid activation whenever they are "needed." The second purpose is, in wartime, far more unsettling than the first.
2. The Actors Behind It: Six Names You Need to Know
Taiwan's cybersecurity community divides the main threat actors targeting Taiwan into several APT groups that already have clear attribution. These are not vague "hacker gangs" — they are state-level cyber units with organizational structure, long-term objectives, and systematic attack plans.
“Taiwan's Cyber Front Line: 2.4 Million Attacks a Day, and the Life-or-Death Speed of Cybersecurity Governance” reports that Timeline of Major APT Incidents(BlackTech Has Lurked for Over 7 Years)。 BlackTech (2010s–), Flax Typhoon (2021–), Volt Typhoon (2019–); Flax Typhoon's targeting of Taiwan is confirmed by an official document, while BlackTech's and Volt Typhoon's targeting of Taiwan rest on industry threat intelligence and intelligence assessments (observation; medium confidence) [3][4][10]。
BlackTech (Ghost Spider)
This is one of the longest-running threats to Taiwan. In September 2023, the U.S. FBI, NSA, and CISA, together with Japan's National Police Agency (NPA) and National center of Incident readiness and Strategy for Cybersecurity (NISC), issued a joint advisory revealing that BlackTech has been infiltrating telecommunications, government, and agencies that support the U.S. and Japanese militaries in Japan and the United States since at least 2010; industry threat intelligence separately indicates that BlackTech has also long targeted Taiwan (observation; medium confidence) [3]. Its methods are especially hard to detect: it breaks into the firmware layer of enterprise network equipment (routers) and plants backdoors there, making it almost invisible to ordinary antivirus software.
What is even more frightening is BlackTech's persistence. Victims often do not discover anything unusual until months, or even years, after being compromised. During that silent window, every email exchanged, every video-conference session, and every confidential document may already have been quietly copied to a remote server.
Flax Typhoon
In August 2023, Microsoft's Threat Intelligence Center (MSTIC) published a report revealing that Flax Typhoon has actively targeted government, education, manufacturing, and information-technology organizations in Taiwan since 2021 [4]. This group's defining trait is "living off the land" — it makes almost no use of custom-built malware, instead relying on legitimate tools built into Windows itself (such as WMI, PowerShell, and net.exe) to achieve lateral movement, which makes its malicious activity extremely hard to distinguish from normal system administration. This leaves traditional signature-based antivirus engines nearly powerless.
Volt Typhoon
In May 2023, the U.S. CISA first issued an advisory revealing that Volt Typhoon typically uses "living off the land" techniques to evade detection [5]; in February 2024, CISA, together with the NSA, FBI, and other agencies, issued a follow-up joint advisory stating that Volt Typhoon had maintained footholds in U.S. communications, energy, transportation, and water critical-infrastructure sectors for at least five years [10]. But this group's intent is not immediate destruction — it is "pre-positioning": establishing a persistent presence inside target systems and waiting to activate it at a specific future moment. The official advisory assesses that its purpose is to prepare for a "major crisis or conflict" with the United States; U.S. officials and some analysts have linked this to the Taiwan Strait situation (inference; medium confidence), but the official documents this article was able to check do not explicitly mention Taiwan. In other words, it is not there to hurt you now — it is there to paralyze you at your most vulnerable moment.
Beyond these three, Mustang Panda focuses on infiltrating government and energy-sector targets; APT41 is a dual-purpose group that combines state missions with cybercrime, with a target range spanning government, energy, communications, emergency response, science parks, and water resources, among other sectors [2]; and UNC3886 targets government agencies and science parks [8]. Together, these six groups make up the primary threat matrix along Taiwan's digital border.
3. The Defenders: What Has the Ministry of Digital Affairs Done in Three Years?
On August 27, 2022, Taiwan's Ministry of Digital Affairs (moda) officially began operations. It is the first cabinet-level ministry in Taiwan's history dedicated to digital affairs, signaling that Taiwan treats cybersecurity as a core national-security issue [6]. Three years on, what has the Ministry of Digital Affairs actually accomplished?
Zero Trust Architecture (ZTA)
This is currently the Ministry of Digital Affairs' most important structural project. The Executive Yuan approved a three-phase rollout plan in 2023, designed to completely flip the old "castle-wall model" (trust anyone once they are inside the internal network) into the zero-trust logic of "never trust, always verify":
- Phase 1 (2023), identity verification: government agencies rolled out two-factor/multi-factor authentication (2FA/MFA) across the board, no longer relying on username and password alone.
- Phase 2 (2024), device verification: devices logging into government systems are assessed for their health status, and non-compliant devices are isolated.
- Phase 3 (2025-2026), application-service trust: implementing the principle of least privilege, with dynamic authorization based on role and context (see the Zero Trust Architecture technical guidance issued by the Ministry of Digital Affairs and the National Institute of Cyber Security; this three-phase timeline does not appear in the text of the Cyber Security Management Act itself).
As of mid-2026, Phase 3 is still underway. The problem is not the technology, but the execution: Taiwan has more than 30,000 government agencies and public-sector units, and their IT capacity varies enormously. County and city governments, and township offices, often have only one or two part-time IT staff, and asking them to simultaneously handle system administration, endpoint protection, and incident response is no less demanding than asking one all-around person to guard an entire large border post alone.
The Cybersecurity Legal Framework
Taiwan passed the Cyber Security Management Act in 2018, making it one of the earlier countries in Asia to establish a systematic cybersecurity legal framework; in 2025 the Act underwent its first amendment since taking effect, strengthening penalties (raising the maximum fine for failing to report to NT$10 million) and mandatory-investigation mechanisms, and shifting the competent authority from the Executive Yuan to the Ministry of Digital Affairs [7]. The law authorizes the Executive Yuan to designate critical infrastructure on a rolling basis; current designations span multiple sectors including energy, water resources, communications, transportation, finance, government agencies, emergency response and hospitals, and science parks, and require operators to undergo regular cybersecurity audits and drills and to report incidents within a specified deadline to the relevant central competent authority (with TWCERT/CC handling coordination in practice).
The law's coverage has one structural blind spot: government IT contractors and software service providers are not subject to mandatory regulation. Attackers know this gap well — rather than mount a frontal assault on a government data center protected by a full WAF (web application firewall), it is easier and stealthier to find a small systems integrator that serves the government and slip a backdoor in through there.
4. The Weak Link: Supply Chains and SMEs
Taiwan's government is rapidly upgrading its direct defenses, but its perimeter — the supply chain — remains a zone of high exposure.
The share of IT budgets that Taiwanese SMEs devote to cybersecurity is widely believed within the industry to be markedly lower than that of large enterprises (observation; low confidence — this reflects industry impression rather than an official, formal statistic; no specific percentage could be traced during this review, and one should be added if a formal Ministry of Digital Affairs industry survey becomes available). This is really a matter of limited resources: a components manufacturer with NT$100 million in annual revenue simply cannot afford a full-time Chief Information Security Officer (CISO) and a round-the-clock Security Operations Center (SOC).
The problem is that this components manufacturer may be supplying a systems integrator, and that integrator's systems connect directly into a government agency's information network. The attacker's path of intrusion runs: small manufacturer → integrator → government agency. The 2020 SolarWinds supply-chain attack is the fullest demonstration of this exact logic at global scale. Taiwan's supply chain is denser and more fragile than the United States' was in the SolarWinds era, yet it still lacks a systemic response of equivalent scale.
Taiwan's government procurement regulations were amended in 2023 to require contractors to meet a specified cybersecurity level, but the rigor and depth of auditing still need to be strengthened. A genuine threat assessment needs to reach through to second- and third-tier suppliers, and that is precisely where the current regulatory mechanism has not yet fully reached.
5. Three Taiwanese Perspectives Converge
The State's Perspective: Treat Cybersecurity Like Weapons Procurement
Cybersecurity protection for critical infrastructure is an urgent national-security issue, not merely an IT governance issue. Volt Typhoon's "pre-positioning" strategy tells us clearly: the point of the attack is not to let you know now, but to hurt you at your most vulnerable moment. Taiwan needs to elevate the cybersecurity level of critical facilities such as electricity, telecommunications, and ports, and treat it as a core defense-budget investment, not routine spending by the Executive Yuan's IT department. (Observation, confidence: high)
The Industry Perspective: Let Semiconductors Lead, and Bring the Whole Supply Chain Along
Major players such as TSMC, ASE, and MediaTek are both high-value targets for attackers and the industry best equipped to build their own cybersecurity defenses in Taiwan. The problem sits upstream and downstream: materials suppliers, packaging and testing houses, and small IC design firms show wildly uneven levels of cybersecurity. The industry should let its major players lead, pushing supply-chain cybersecurity certification as an entry requirement rather than leaving it as a voluntary guideline. This is not just an ethical question — it is a question of TSMC's own supply-chain resilience. (Observation, confidence: high)
The SME Perspective: Cybersecurity Isn't IT's Job — It's Every Person Who Opens an Email
As government contractors and technology suppliers, SMEs are the most overlooked link in the attack chain. The government's free cybersecurity checkups (offered by the Ministry of Digital Affairs) should be expanded significantly in coverage, and the application threshold should be lowered further. More fundamentally, this requires a cultural shift: a large proportion of Taiwan's cybersecurity incidents stem from human factors — opening phishing emails, using weak passwords, ignoring software-update prompts. This is not a technology problem, it is a habit problem, and it needs to start with awareness training that runs from rank-and-file civil servants to corporate employees. (Observation, confidence: high)
Sources
- National Security Bureau — Full Report: "Analysis of Chinese Communist Cyberattack Patterns Against Taiwan, 2024"
- National Security Bureau — "Analysis of Chinese Communist Cyber Threats to Taiwan's Critical Infrastructure, 2025"
- CISA / NSA / FBI / Japan National Police Agency — BlackTech Joint Cybersecurity Advisory AA23-270A
- Microsoft Threat Intelligence — Flax Typhoon Using Legitimate Software to Quietly Access Taiwanese Organizations
- CISA — Volt Typhoon Joint Advisory AA23-144A (Living-off-the-Land Techniques Evading Detection)
- Administration for Cyber Security, Ministry of Digital Affairs — Official Website (Policy and Regulations Section)
- Laws & Regulations Database of the Republic of China (Taiwan) — Cyber Security Management Act
- Google Cloud (Mandiant) — Cloaked and Covert: Uncovering UNC3886 Espionage Operations
- TWCERT/CC — Official Website and Cybersecurity Intelligence Newsletter (originally cited as the "2024 Annual Report"; no document by that name could be found, replaced with the official portal)
- CISA / NSA / FBI, and Other Agencies — Follow-Up Joint Cybersecurity Advisory on Volt Typhoon, AA24-038A
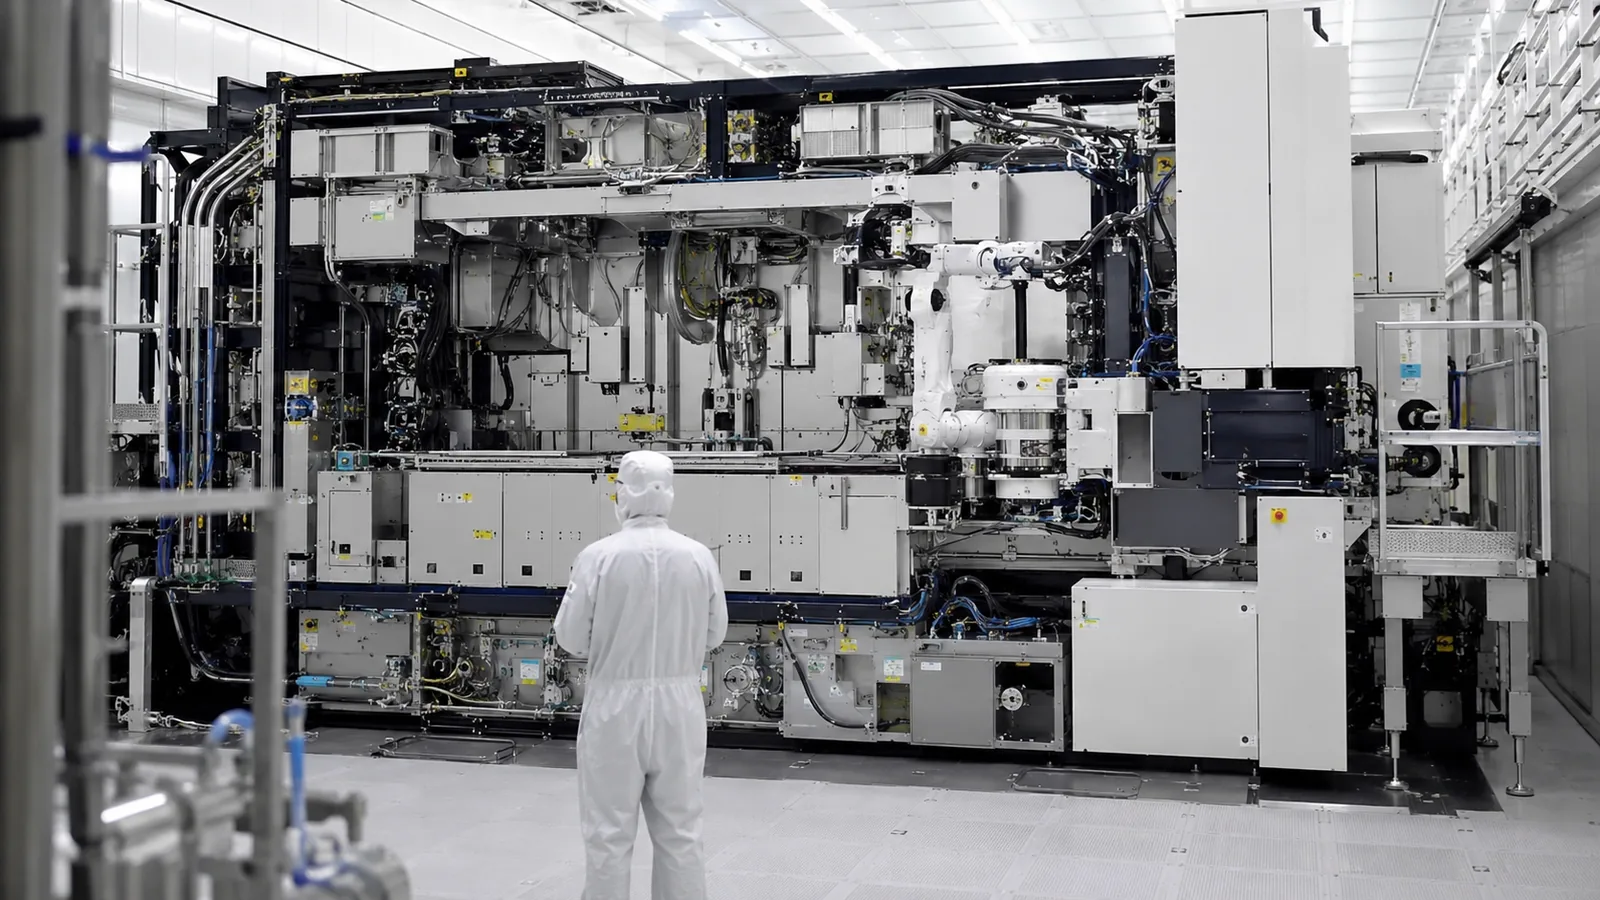
The Equipment Bind: Taiwan's Dependence on ASML, KLA, and Applied Materials
Taiwan makes more than 92% of the world's most advanced chips, but the EUV machines, etch tools, and metrology systems that make it possible come almost entirely from the Netherlands and the United States — down to the remote shutdown button, which is also held by someone else. That dependence is Taiwan's talisman, and the least-discussed blade hanging over the silicon shield.
Taiwan's Two Faces
The whole world depends on Taiwan's chips — and is quietly preparing for the day it might lose them. The same island is both the heart of the supply chain and a geopolitical powder keg. How can Taiwan's companies turn "irreplaceable" into an advantage that lasts?